Top Ways to Prevent Data Loss
Data loss is a daily risk for businesses, and proper protection is critical. Data breaches can cost organizations millions per incident, and as businesses become increasingly data-dependent, the stakes of poor security continue to rise.
Fortunately, there are proven ways to keep your data safe. By taking preventive action, your company can avoid massive financial penalties, maintain its reputation and ensure regulatory compliance. Explore how to prevent data loss in your company’s operations.
Understanding Data Loss in the Modern Landscape
Data loss takes several forms. It can be unintentional, such as someone spilling a cup of coffee on their computer, or intentional, such as a bad actor breaking into your company’s system. Data loss occurs when information is deleted, corrupted or otherwise unrecoverable.
Today, companies are especially vulnerable to data loss because of cloud adoption, remote work and AI-powered attacks. Whether due to human error or cybersecurity threats, data loss has become harder to combat. In fact, nearly 94 million records were leaked in the second quarter of 2025 alone.
These incidents can lead to significant revenue loss, operational disruption and regulatory penalties. Diverse data loss prevention techniques are necessary because data loss occurs in various ways.
10 Data Loss Prevention Strategies
Preventing data loss calls for a multilayered approach. Every organization faces different risks, but the following best practices help your company improve data resilience. Here are several things you can do to keep your information secure.
1. Implement a Zero Trust Model
Zero Trust architecture operates under the principle of “never trust, always verify.” This security approach treats every access request as a potential threat.
Implementing a Zero Trust model involves:
- Evaluating the threat surface: Identify the highest-risk data that hackers could target. Focus on your company’s most critical applications, assets and services.
- Mapping how data flows across your network: Assess network transactions to verify that only the right users have access to sensitive information. Understanding data traffic will help you determine where to place enforcement points.
- Architecting a framework: Implement identity-based controls to keep data from falling into the wrong hands. This specialized network will segment and secure zones to limit lateral movement.
- Monitoring and maintenance: Continue analyzing user activity in real time. Maintenance is essential, as it lets you spot vulnerabilities and adjust policies as threats change.
2. Protect Your Cloud Data
Cloud misconfigurations are a common cause of data leakage. To strengthen cloud protection, implement identity and access management, enable network segmentation and establish secure key management practices.
Maintain AES-256 data encryption and perform regular audits using cloud security posture management (CSPM) tools. This way, you can identify and mitigate misconfigurations before they become an issue. This proactive approach supports compliance with the General Data Protection Regulation (GDPR) and the Health Insurance Portability and Accountability Act (HIPAA). It also helps protect against ransomware.
3. Create an Incident Response Plan
Your organization should develop a system security plan to safeguard its assets from breaches and associated damage. A formal incident response plan will outline communication strategies and containment procedures.
Key elements of an incident response plan include:
- Appointing a dedicated response team with clearly defined roles.
- Performing risk assessments to identify breach severity.
- Preparing communication protocols for notifying stakeholders.
- Conducting post-incident reviews to prevent further breaches.
4. Mandate Multi-Factor Authentication
Multi-factor authentication (MFA) is one of the most effective controls to prevent unauthorized access. This framework requires users to provide verification beyond their passwords.
MFA combines something you know (password), something you have (a phone or token) and/or something you are (biometrics). To keep important information secure, mandate MFA across all critical systems and administrative interfaces.
5. Encrypt Data in Transit and at Rest
Comprehensive encryption protects data in two states:
- At rest: Data stored on physical media, databases or cloud storage.
- In transit: Data moving between systems.
Both are essential for data security and HIPAA compliance.
Encryption at rest protects against unauthorized access or physical drive theft. You can do this with methods like transparent data, full disk and file-level encryption. You’ll also want to implement AES-256 encryption standards.
Encryption in transit protects data as it moves across your network. Primary threats include interception or eavesdropping. To protect active data, use transport layer security, hypertext transfer protocol secure (HTTPS) and virtual private networks (VPNs).
6. Train Employees on Data Security
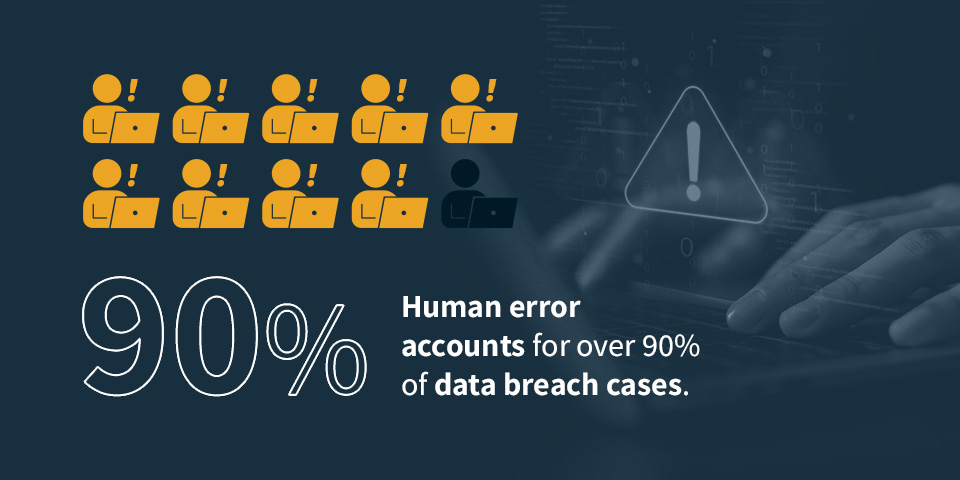
As companies shift toward remote work environments, the risk of security breaches is at an all-time high. Human error accounts for over 90% of data breach cases. Proper security training is an essential part of data loss prevention.
Regular training exercises can help employees recognize and thwart cyber threats. Implement new guidelines, phishing recognition, password hygiene, learning activities, role-based training programs and success monitoring to strengthen awareness.
An insider threat mitigation program can also help employees recognize behavioral indicators. Given that insider risks cost an average of $16.2 million per organization, investing in training delivers substantial return on investment (ROI).
7. Automate Data Backups
Automated backups eliminate human error and ensure consistent data copies for quick recovery. The 3-2-1 rule remains the gold standard — three copies of data on two different media types, with one copy off-site.
However, backups lose their value without regular recovery testing. Develop a comprehensive data backup strategy with copies resistant to ransomware. The right backup storage solutions can help support a reliable recovery.
8. Monitor Endpoint Devices
Many successful breaches originate at endpoint devices such as laptops and phones. Mobile device management solutions provide centralized control over corporate and employee-owned devices. This can look like remote locking, app distribution and policy enforcement.
Continuous monitoring detects unauthorized access attempts and risky user behavior. Always address the complete device life cycle to prevent data recovery from discarded devices.
9. Develop a Vendor Risk Management Policy
Organizations often experience breaches due to third-party data access. A strict Vendor Risk Management policy prevents these breaches by placing security controls over external partners.
This policy should mandate pre-onboarding security assessments and regular audits. Require vendor encryption, restrict access to necessary data and ensure your incident response plan meets your standards.
10. Use Data Loss Prevention Software
Data loss prevention (DLP) software offers visibility into how sensitive data is accessed and transferred. This software enforces security policies to prevent unauthorized sharing. DLP solutions classify data by sensitivity, then establish rules to ensure proper transmission.
Modern platforms can integrate with cloud services, email systems and endpoints. DLP software monitors data movement across hybrid environments, supporting GDPR and HIPAA compliance and protecting intellectual property.
Frequently Asked Questions About Data Loss
Understanding the full scope of data protection is essential. Here are answers to the most common questions about data loss.
What Is the Most Common Cause of Data Loss?
Two of the most common causes of data loss are human error and physical hardware failures. Human errors, including accidental deletion, misconfiguration and phishing attacks, are often cited as the largest threat.
How Does Data Loss Prevention Differ From Data Backup?
Data loss prevention and data backup serve complementary roles. DLP is proactive, combining access controls and monitoring to prevent unauthorized access. Data backup is reactive, offering recovery after data deletion, corruption or ransomware. Organizations need DLP to minimize breaches, and they require backups for quick recovery when prevention fails.
What Are the First Steps To Take After a Data Loss Event?
After a data loss incident, set your incident response plan into action:
- Stop additional data loss by taking affected systems offline.
- Secure physical areas and remove posted information from the web if applicable.
- Identify compromised data and determine whether sensitive information was exposed.
- Communicate with your response team, legal counsel and potentially law enforcement.
Work With DataSpan to Build Your Data Loss Prevention Strategy
Data loss prevention calls for a multipronged approach that incorporates employee training, company policies and multiple backups. For over 50 years, DataSpan has helped organizations implement data protection solutions tailored to their specific needs. We offer cloud-based storage and off-site data centers to help you back up and protect your company’s most sensitive information.
Ready to create a data loss prevention strategy? Find your local rep or contact us today to learn more.
About the Author: Alex von Hassler’s long term focus is the continued testing, learning, and deployment of modern IT solutions. During his years as a DataSpan team member, his responsibilities grew from managing Salesforce CRM to improving system security, creating marketing initiatives, as well as providing continued support to the highly motivated and experienced team in an ever-changing industry. As DataSpan evolves to provide the best-fitting IT solutions to its customers, Alex von Hassler continues to hone his skills in the world of web-based ERP systems, security, and best customer engagement practices. Empowering such a dynamic team with the right tools provides him with enormous gratification.